

Table of contents

The 4 best AI agent authentication tools in 2026

Jon Gitlin
As you help users connect your AI agents to MCP servers, you’ll need to implement authentication flows that prevent unauthorized access and protect sensitive information.
Developing and maintaining these authentication flows yourself likely isn’t sustainable; it means investing time and resources into security infrastructure that distracts from your core product work.
To that end, we’ll walk you through several tools that allow your users to authenticate AI agents effectively and quickly.
Merge
Merge Agent Handler uses Merge Link, an embeddable UI component, to help users authenticate with a given connector.
For example, say a user asks your AI agent to create a ticket in their project management system.
Merge Agent Handler can check if the user has the appropriate access to the project management system. If they don’t, Merge Agent Handler surfaces Merge Link; if they do, the agent goes on to perform the requested action.
Pros of authenticating with Merge Agent Handler:
- Comprehensive authentication and access controls: Our example above oversimplified the authentication process
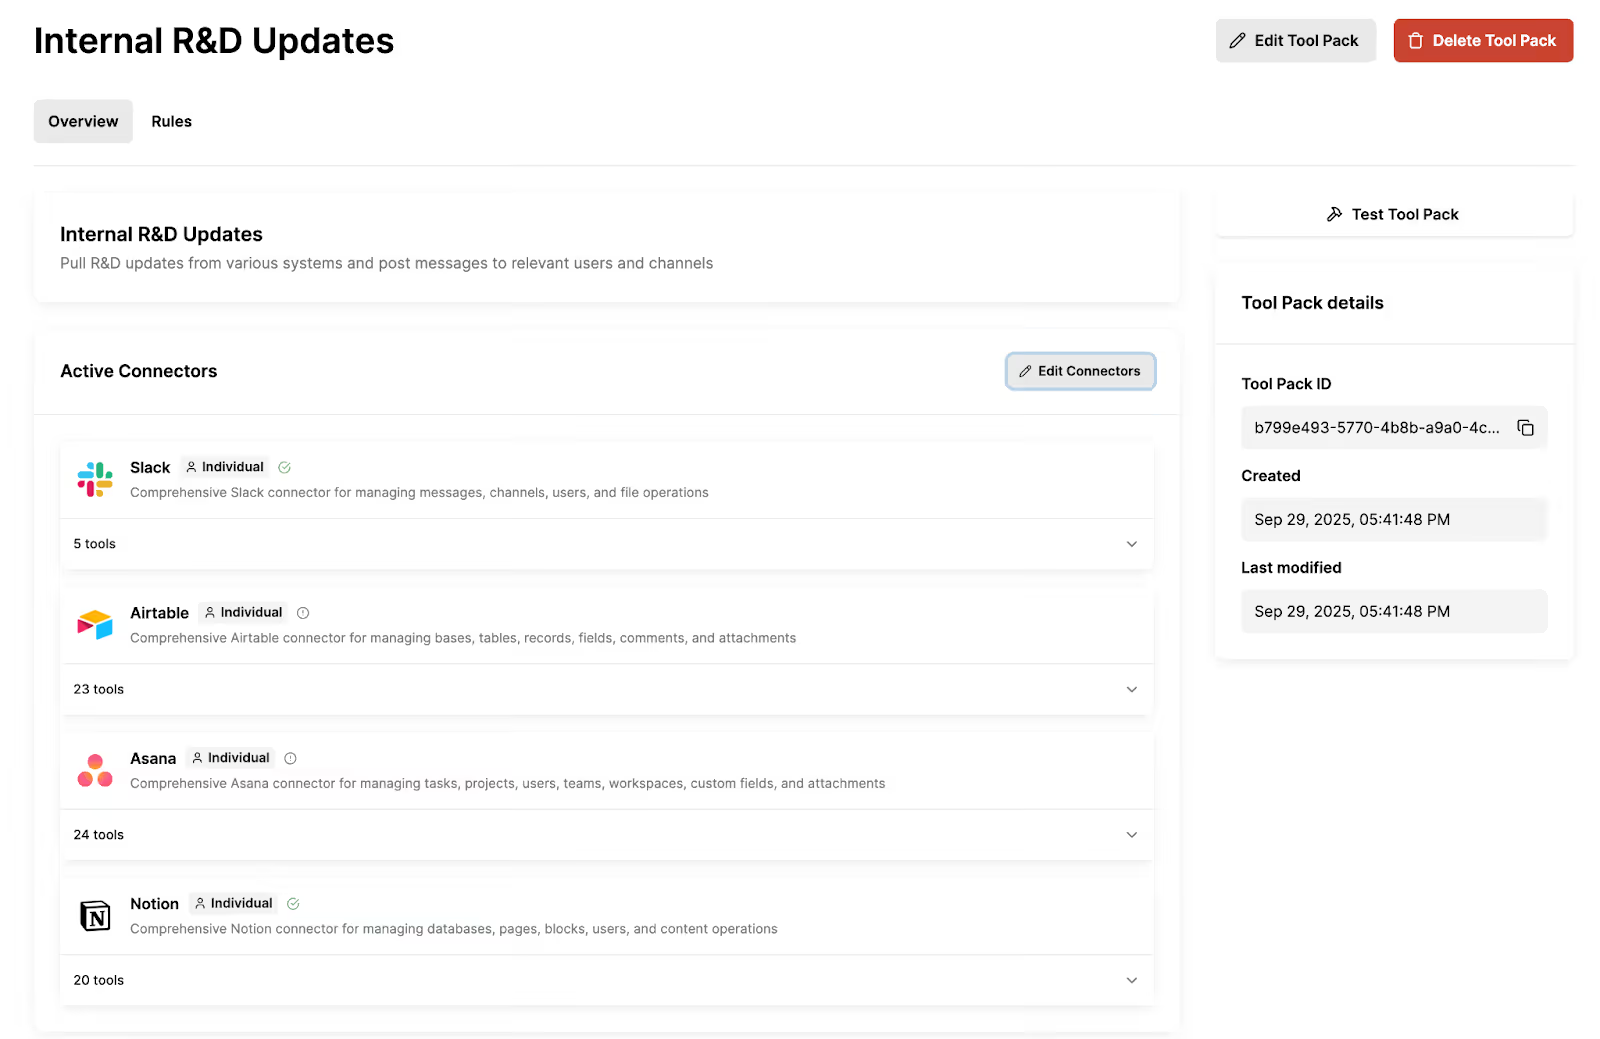
Behind the scenes, Merge Agent Handler lets you organize connectors and tools into Tool Packs. You can then register users (representing individuals or service accounts) and link them to those Tool Packs using shared or individual authentication credentials, each with precisely defined access scopes.
- Intuitive and seamless auth experience for users: The process of authenticating with Merge Link is incredibly simple for users, as Merge Link provides instructions and relevant links every step of the way. This leads to high success rates for authenticating and authorizing users and faster adoption of your AI agents

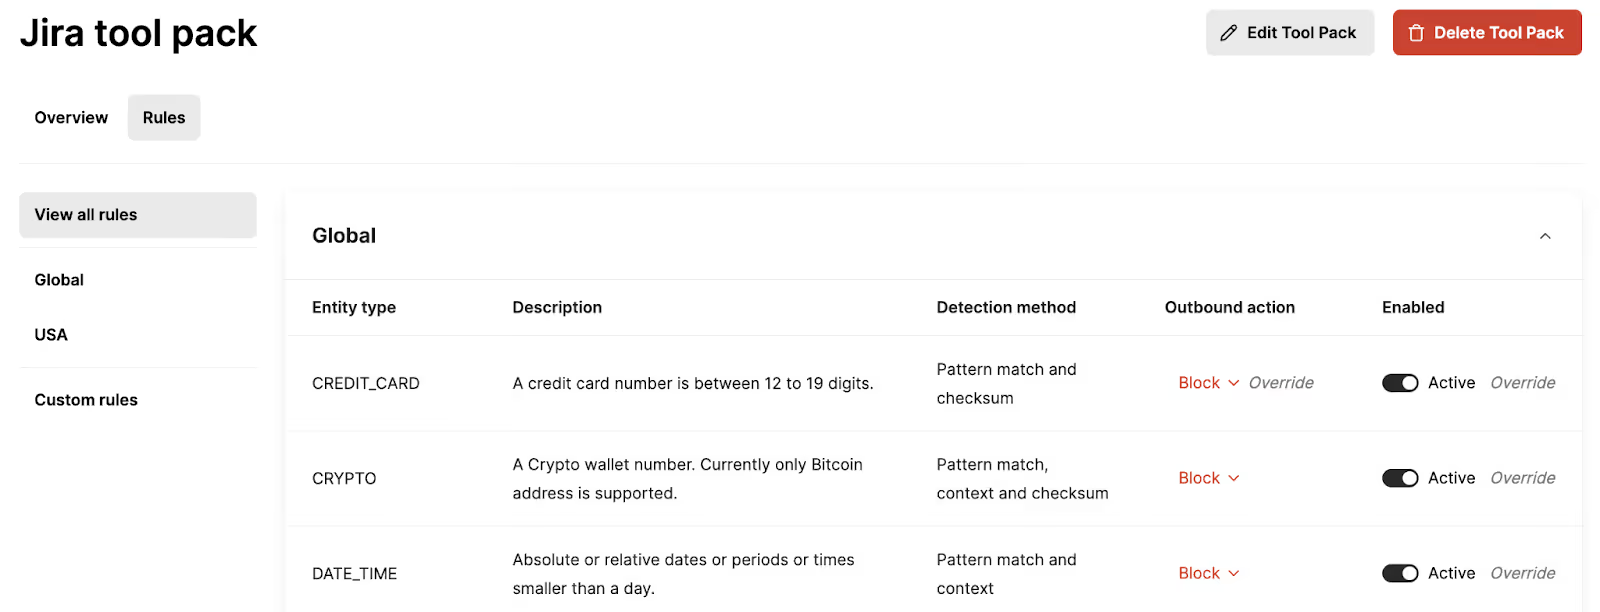
- Additional features and capabilities to keep data secure: Merge Agent Handler also lets you set rules on the data types your agents can and can’t share, track violations of these rules via alerts, use logs to diagnose and troubleshoot issues, and more
Composio
Composio takes a configuration-based approach to manage authentication for each connector.
Here’s how it generally works:
1. Creating and storing auth configs: Each connector has its own authentication “config.” You can define and store these configs in Composio to manage how users connect their accounts.
2. Authenticating the user: When a user connects to a toolkit (or a collection of pre-built tools), Composio handles the full OAuth flow and returns an auth config ID tied to that user’s credentials.
3. Running actions with the right credentials: To execute any action, you’d pass both the user ID and the auth config ID. Composio uses these to ensure the correct account and permissions are applied.
Pros of authenticating with Composio:
- Centralized and reusable auth management: You don’t have to build or maintain separate auth logic for GitHub, Slack, Notion, etc. Once a user authenticates, you get a reusable auth config id that works across your app and agents
- Managed credential storage & lifecycle: Composio handles the storage, refresh, and usage of access/refresh tokens on behalf of your app (when using its managed auth), so you don’t need to build your own token vault
- Simple API for multi-user and multi-connector scenarios: By passing both the user id and auth config id, you can easily handle multiple users using the same connector (e.g., multiple GitHub accounts) and one user connected to several connectors
Cons of authenticating with Composio:
- Manual, SDK-centric testing workflow: To validate a given auth flow, you’d need to use scripts; this excludes non-engineers from testing and makes it harder to scale auth tests
- Access variability post-authentication: Even if a user authenticates successfully, they may not be able to make certain tool calls based on their plan (i.e., "premium tool" usage is constrained on lower tier plans). This can lead to a confusing and frustrating user experience
- Limited authentication visibility post set-up: If and when authenticated toolkits are disconnected, Composio doesn’t provide the real-time alerts necessary to notify the relevant users and allow them to re-authenticate quickly
Related: The best alternatives to Composio
Arcade
Similar to Merge Agent Handler, when a user asks your AI agent to perform an action, Arcade verifies whether that user has granted the necessary permissions (scopes) to complete the request.
If the required scopes haven’t been authorized, Arcade automatically initiates an OAuth flow, prompting the user to authenticate and grant access; if authorized successfully, Arcade securely manages and reuses that authorization for future requests so the user doesn’t need to re-authenticate each time.
Pros of authenticating with Arcade:
- Support for multiple authentication methods: Arcade supports OAuth 2.0, API keys, and user tokens, ensuring that every potential tool can be authenticated
- Authentication during task-execution: By verifying the user's identity at the moment of authentication, Arcade ensures tokens are only granted to the legitimate user
- Strong leadership background in authentication: Their founding team has helped build authentication products (e.g., Stormpath); given their team’s expertise in securing applications and data, Arcade will likely continue to be a strong solution for authenticating AI agents
Related: Arcade.dev's top competitors
Cons of authenticating with Arcade:
- Access variability post-authentication: Like Composio, Arcade prices their tools differently (some are “basic tools” while others are “advanced tools”). This can lead to tool calls failing for users that aren’t on the right plan
- Limited track record: Arcade has only received seed funding, was founded in 2024, and has a limited customer base. As a result, their auth implementations may not be fully battle tested and scalable
- Insecure community MCP servers. Several of Arcade’s community MCP servers may skip proper authentication workflows, leading your agents to grant unauthorized access to sensitive data
AgentID
The three tools above authenticate your agent into someone else's systems. AgentID handles the other direction: an agent shows up at your product and needs to sign in.
It's a standard OpenID Connect provider at auth.agentid.com, added like Google or GitHub login using the authorization code flow with PKCE. The agent runs the flow itself, and your app gets an ES256-signed ID token identifying that agent, plus the email of the human accountable for it.
Any app can accept AgentID sign-ins without registering, which returns the openid, email and profile scopes. Registering in the AgentID console or CLI unlocks owner_profile and owner_email. If the agent can't share its owner, the organization owner approves the claim instead.
Pros of authenticating with AgentID:
- The agent is a principal, not a delegate: Other tools answer "can this agent act inside this user's Salesforce." AgentID answers "who is this agent that just hit my signup page."
- You learn the accountable human: Registered apps get
owner_email, so an autonomous sign-in still leaves a person to contact, invoice, or ban. - Nothing proprietary: It's OIDC with standard discovery, so your existing social login library works. No SDK needed.
- Agent keys stay with the agent: A P-256 keypair is generated in the browser during enrollment. AgentMail stores only the public key, and each key works only for its own agent.
- Disclosure the agent has to accept: The first sign-in shows the claimed scopes and the agent approves with its own key. Approval lasts 180 days per inbox and app.
Cons of authenticating with AgentID:
- Inbound sign-in only: It won't get your agent into a user's Gmail or PM tool, so most teams need something like Agent Handler alongside it.
- Needs an AgentMail inbox: The agent must be provisioned through AgentMail, so it's not neutral across agent stacks.
- Very new: Launches publicly October 6, 2026, with no production track record yet.
AI agent authentication FAQ
In case you have any more questions on authenticating AI agents, we’ve addressed several more below.
What companies provide authentication for AI agents?
A wide range of companies provide authentication support for agents, includng Merge, Arcade, Composio, Nango, and WorkOS.
Merge’s Agent Handler solution stands by providing the most reliable, enterprise-grade MCP connectors. And it provides an end-to-end platform; it allows you to not only authenticate your agents but also test their tool calls, monitor their tool interactions in production, set up and use rule-based alerts, and more.
Should I build my own agent authentication or use a managed provider?
You should default to using a managed provider because setting up agent auth isn’t just wiring up OAuth. An in-house build requires your engineering team to quickly end up owning a long list of hard problems that go beyond “get a token and call an API.” This'll distract your team from core projects, like building and improving on your company’s agents.
Here are just a few items that need to get built:
- Auditability and production-grade observability: You’ll need to answer “what happened, who authorized it, and what data was touched” for every agent action
- Least-privilege access and centralized governance: Even if OAuth works, you’ll still ask, “Which agents can do what, in which tools, under which conditions?”
- Secrets management and ongoing credential operations: Building auth requires building secure storage, token refresh behavior, key rotation, revocation, and incident response playbooks
How are access tokens stored, rotated, and refreshed for AI agents?
The process differs depending on whether you use a managed provider or build auth in-house. Assuming you use the latter, here’s how it’d typically work:
- OAuth credentials get stored centrally and encrypted at rest: A managed provider stores the credentials in its backend with layered encryption. Tokens can also be stored with multiple layers of encryption, with the database encrypted and sensitive columns additionally protected with envelope encryption
- Refreshed automatically as needed: When an agent runs a tool call, the provider resolves the right credential for the relevant user or shared scope and uses it to execute the request. If the access token is expired, the provider uses the refresh token to mint a new access token and proceeds, so the agent doesn't need to implement refresh logic
- Rotated and revoked through a few levers: The provider manages credential lifecycle centrally (so tokens are not distributed to end users). For access into the provider (e.g., an MCP endpoint), your agent uses an API key you rotate in your own secrets manager. For third-party OAuth, access can be revoked by removing consent, which forces re-authentication
Jon Gitlin


Authenticate your AI Agents with ease via Merge Agent Handler
Leverage Merge Agent Handler to securely connect your agents to thousands of pre-built tools, as well as manage and monitor all tool interactions.


But Merge isn’t just a Unified
API product. Merge is an integration platform to also manage customer integrations. gradient text
But Merge isn’t just a Unified
API product. Merge is an integration platform to also manage customer integrations. gradient text
But Merge isn’t just a Unified
API product. Merge is an integration platform to also manage customer integrations. gradient text
But Merge isn’t just a Unified
API product. Merge is an integration platform to also manage customer integrations. gradient text